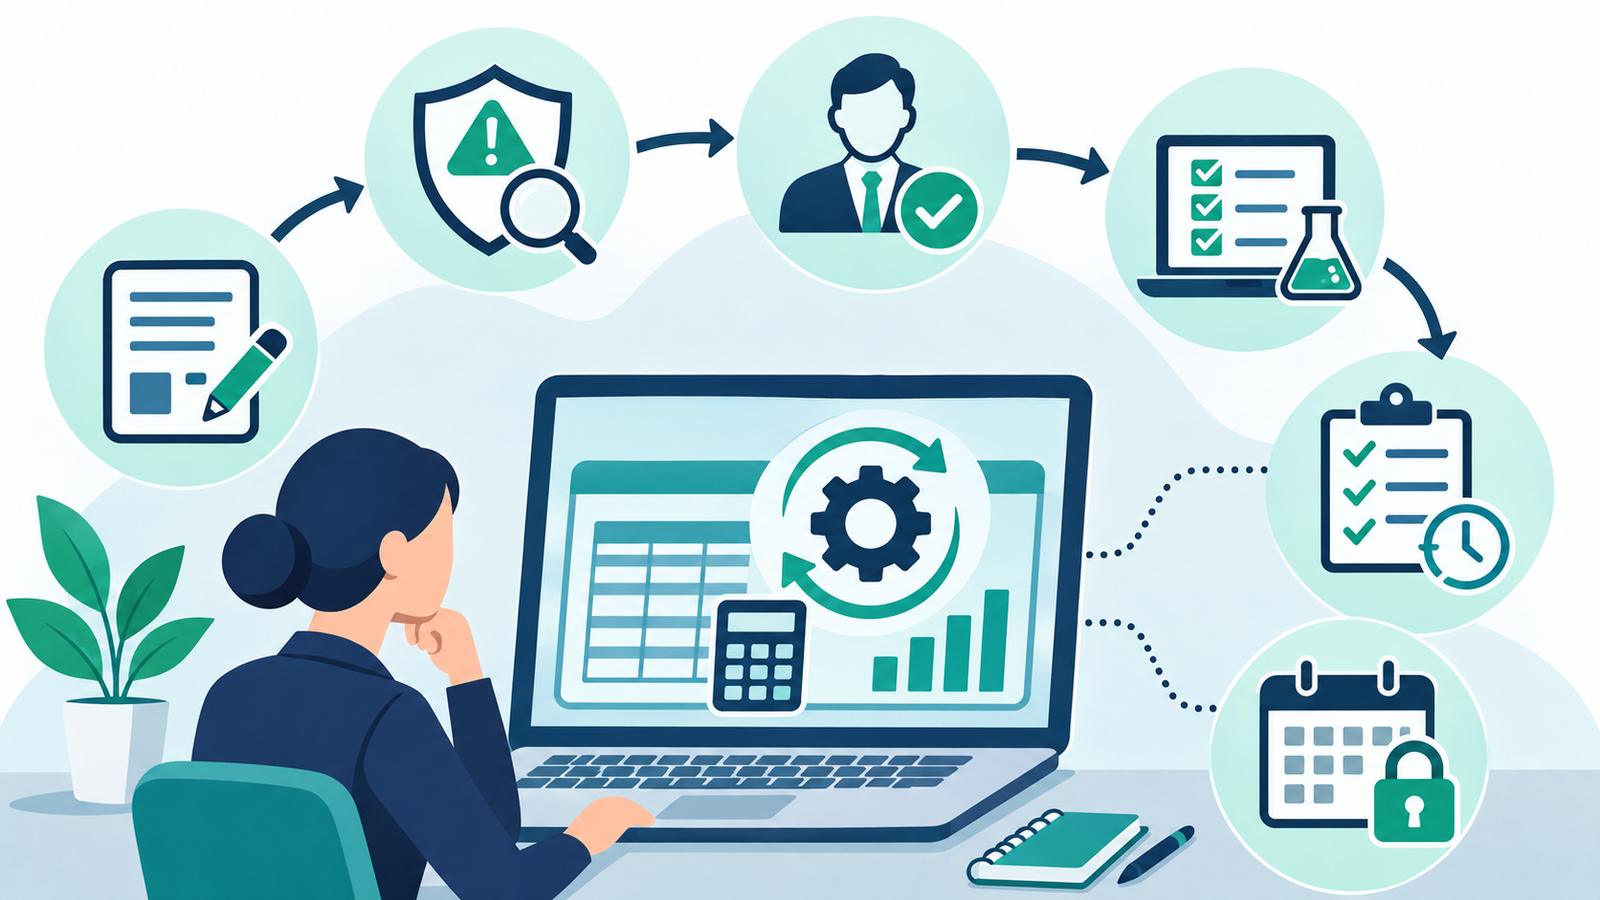
Direct answer: Accounting-system changes should be requested by a named business owner, reviewed for accounting, security and workflow impact, approved within documented authority, implemented by an authorised user and tested by someone who can verify the result. Sensitive changes should not depend on one person acting without review.
This general guide is for Australian small-business owners, including Epping, Melbourne and Victoria. Confirm current rules and product settings for your circumstances.
Which changes need formal approval?
Use a controlled process for user roles, bank details, tax settings, chart-of-accounts changes, rules, integrations, lock dates, conversion balances and reporting mappings. Set risk thresholds so routine corrections and high-impact changes do not follow the same path.
Who should review accounting and security impacts?
Assign reviewers who understand the affected ledger, reporting obligation and system access. The owner should confirm business purpose; a knowledgeable accounting reviewer should assess treatment; and an authorised administrator should assess permissions and implementation.
What evidence should support approval?
Retain the request, reason, affected period, proposed change, risk assessment, approver, implementation date, test result and rollback or correction plan. Xero history and notes can help identify who changed financial data and when.
How should closed periods be protected?
Use lock dates where appropriate and restrict who may reopen a reviewed period. Xero’s financial-settings guidance explains that administrators control lock dates. Reopening should trigger a check of reports, lodged figures and downstream integrations.
How should emergency changes be handled?
An urgent change still needs a recorded reason, temporary authority, evidence of testing and prompt retrospective review. Do not allow urgency to become a permanent bypass around owner control.
What belongs in the practical checklist?
- Change request and business purpose
- Affected data, reports and obligations
- Risk and segregation-of-duties review
- Named approver within delegated authority
- Authorised implementer and scheduled timing
- Testing and evidence of expected result
- Audit history and period-impact review
- Rollback, follow-up and closure approval
What could this look like in practice?
Hypothetical example: A hypothetical Epping retailer needs a new bank-feed mapping. The bookkeeper proposes the change, the owner approves the business purpose, an administrator implements it, and another reviewer tests source totals and the clearing account. These invented facts illustrate control steps.
What do business owners ask?
Can the system administrator approve every change?
Not necessarily. Administrator access permits action; business and accounting authority should be documented separately.
Should every correction wait for a committee?
No. Define proportionate authority levels, but retain traceable approval for sensitive changes.
Does an audit log prove the change was correct?
No. It records activity; the business still needs evidence, testing and an accounting review.
Where can you continue?
Read the live parent guide, review service information, and explore the TNS Accounting homepage.
Which official sources were checked?
- Xero: financial settings and lock dates
- Xero: history and notes report
- Xero: keep business data secure
Published by TNS Accounting. Official sources checked 20 November 2026. Rules, guidance and software features can change; confirm the linked sources before acting.