
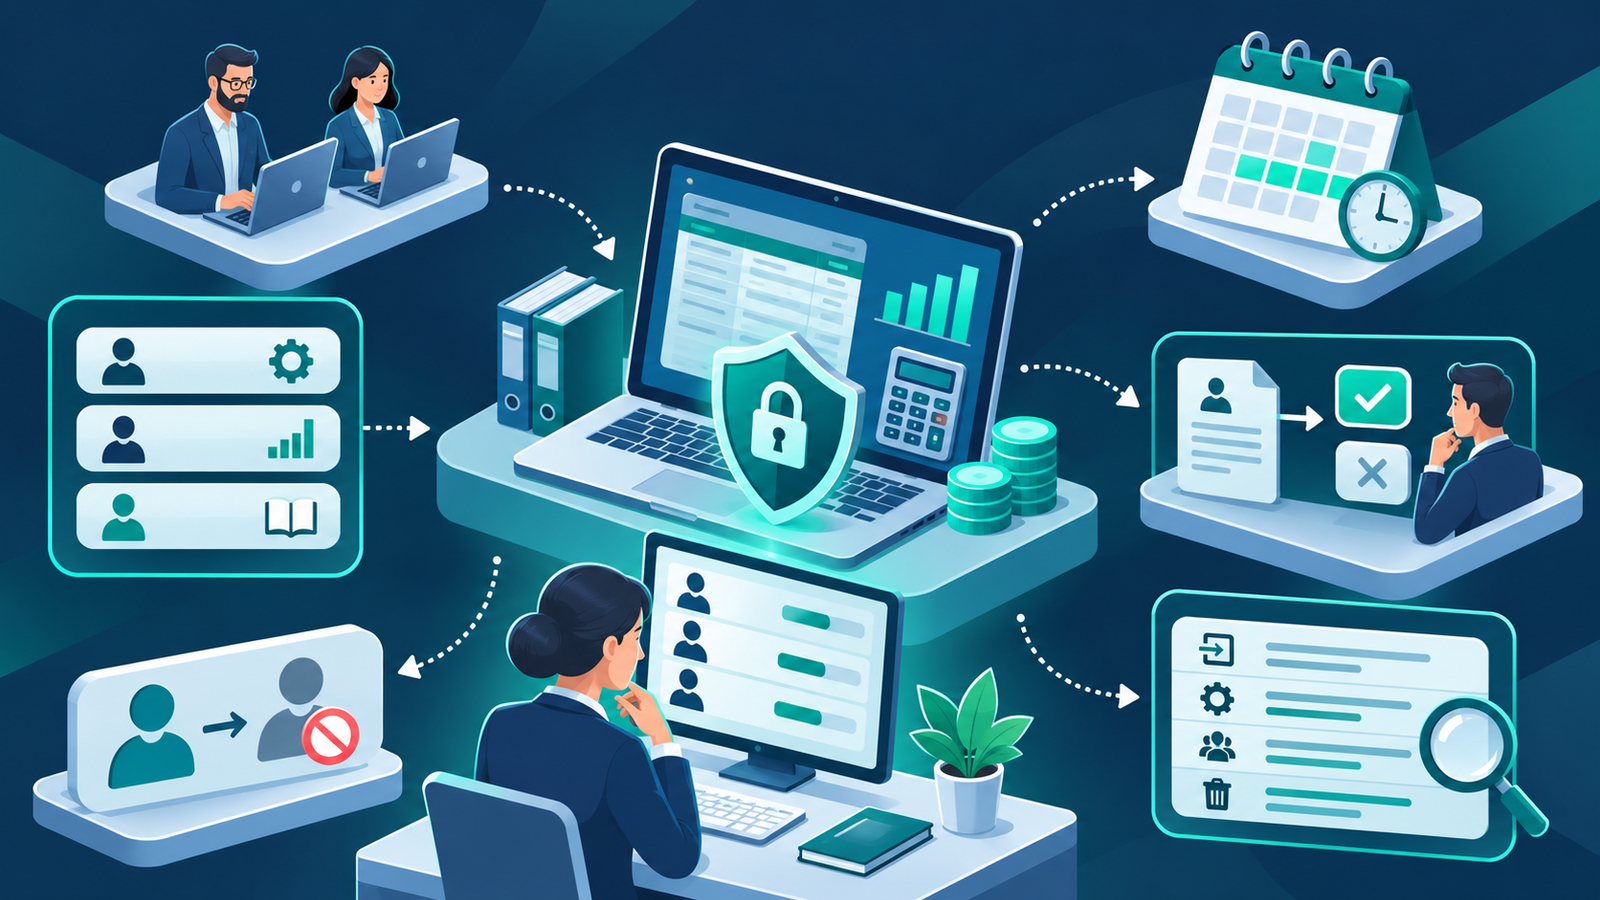
Direct answer: Owners should give each provider a named account with the least access needed, multi-factor authentication where available, an approved purpose, start and review dates, and a clear removal trigger. Shared logins make activity harder to attribute and should be avoided.
This general guide is for Australian small-business owners, including Epping, Melbourne and Victoria. Confirm current rules and software settings for your circumstances.
Which provider details should the access register hold?
Record the person, organisation, role, systems, access level, business purpose, approver, start date, next review and expiry or removal event. Avoid generic labels that hide who actually used the account.
How should the right permission level be chosen?
Map the provider task to the smallest available role. Separate viewing, transaction entry, payroll, banking, user administration and application connections where the software allows it.
Which security controls should be mandatory?
Use individual accounts, strong authentication and a verified recovery process. The ATO recommends reviewing who can access business information and removing access that is no longer required.
How should provider activity be reviewed?
Check user history, configuration changes, connected apps, exports, unusual journals and reopened periods. Investigate exceptions with the provider and retain the closure evidence.
When should access be removed?
Remove or reduce access when the task ends, a person leaves the provider, the engagement changes or a security concern arises. Confirm ownership of files, integrations and administrator recovery before handover.
What belongs in the practical checklist?
- Named provider user
- Approved business purpose
- Least-privilege role
- MFA or strongest available control
- Start, review and expiry dates
- Activity and change review
- Removal trigger and owner
- Handover and recovery access tested
What could this look like in practice?
Hypothetical example: A hypothetical Melbourne wholesaler gives a software consultant temporary configuration access for an integration. The owner approves the role, reviews the activity history after testing and removes the account at project completion. This invented example is not a software guarantee.
What do business owners ask?
Can a provider use the owner’s login?
Individual access is safer for attribution and removal; use supported named-user roles instead.
Should provider access expire automatically?
Use expiry where available and still review access after the task or engagement changes.
Who should own the main administrator account?
The business should retain recoverable ownership and avoid depending entirely on an external provider.
Where can you continue?
Read the live parent guide, review service information, use the related owner system-management review guide, and explore the TNS Accounting homepage.
Which official sources were checked?
- ATO: review access to business information
- Xero: keep business data secure
- Xero: user roles and permissions
Published by TNS Accounting. Official sources checked 21 November 2026. Rules, guidance and software features can change; confirm the linked sources before acting.






